Trigger
Human speedWaits for Patch Tuesday or the quarterly scan.
Machine speed
An advisory or known-exploited listing starts a run in minutes.AI transformation · AIOps
Exploits arrive within hours of a patch, and routine tickets wait days in queues and hand-offs. Silex puts AI agents into your L1 and L2 queues. They investigate every alert and request, draft the fix, and apply it through Ansible Automation Platform. People approve and audit instead of executing each step.
Why now
Turning a patch into an attack once took weeks. In 2026 it takes hours, and a frontier model can write a working exploit from a patch in under an hour. Remediation still runs on a monthly cycle.
The L1 and L2 queue
Most operational tickets need an hour of work or less. They wait to be picked up, then wait again at every hand-off. With the platform, the agent does the work around the decision, and your people make the decision.
The result
Your engineers approve and audit instead of gathering and typing. The approval step doesn't change: the same people approve in the same tool.
Machine speed
The person does not disappear. Their role changes from executing each step to approving and auditing.
| Step | Human speed · the monthly cycle | Machine speed · the continuous loop |
|---|---|---|
| Trigger | Waits for Patch Tuesday or the quarterly scan. | An advisory or known-exploited listing starts a run in minutes. |
| Playbook authoring | Engineers write and test scripts by hand, over days. | The agent drafts, lints, and canary-tests the playbook in the same run. |
| Baseline | Rarely taken. Drift is found by the outage. | Every host is recorded before each change: packages, services, trust stores, SELinux settings. |
| Approval | A change board that meets weekly. | Pre-approved paths. A person approves each action in the ticket, with a full audit trail. |
| Verification | Rescan next cycle. A failed fix waits a month. | Rescan in the same run. A failed fix is rolled back or reopened at once. |
| Exposure window | Weeks, from advisory to fix. | Hours, matching the attacker's clock. |
Machine speed
An advisory or known-exploited listing starts a run in minutes.Machine speed
The agent drafts, lints, and canary-tests the playbook in the same run.Machine speed
Every host is recorded before each change: packages, services, trust stores, SELinux settings.Machine speed
Pre-approved paths. A person approves each action in the ticket, with a full audit trail.Machine speed
Rescan in the same run. A failed fix is rolled back or reopened at once.Machine speed
Hours, matching the attacker's clock.One ticket, start to finish
A ticket asks for an application tier to be patched. The agent learns the environment, files the change in ServiceNow, and waits. Once a person approves, Ansible Automation Platform patches the idle node first, the agent checks it, finishes the tier, and resolves the ticket.
Every step, read, and job is in the run's record.
DoneThe application tier is patched and the ticket is resolved.
Where agents help first
Each workflow covers the alert and request types agreed for it, and anything else goes back to the queue. Each card shows the autonomy a workflow can reach; every one starts read-only.
Assist
Alerts from your monitoring tools, correlated with logs and the CMDB and diagnosed read-only. The lowest-risk place to start.
Up to self-heal
Disk cleanup and expansion, service restarts, certificates, and reboots, planned, approved, and verified.
Up to self-heal
A baseline before each change, staged execution with a health check, verification, and a diagnosis of anything that fails.
Act with approval
Builds through your pipeline and AAP, drafted as pull requests, with a separate approval for anything that spends money.
Act with approval
Databases, schemas, grants, and space additions from your service catalog.
Assist
Device changes checked against the approved change, its window, and your CMDB.
Act with approval
Dependency checks, a staged power-off, and a hold before anything destructive.
Act with approval
Per-host fixes and CVE campaigns from your vulnerability scanners, with the evidence drafted alongside.
How it works
The same loop drives triage, remediation, patching, and provisioning. Every read and every change passes the platform's gateways, and every change is held to the plan a person approved.
A ticket, alert, or advisory lands in your ITSM queue, and the platform starts a run for it.
The agent reads monitoring, logs, and the CMDB through the enforcement gateway, from a sandbox with no real credentials.
It posts its findings to the ticket and proposes a plan. A playbook it writes goes to review as a pull request.
A person approves the change in your ITSM. Nothing runs while it waits.
Ansible Automation Platform runs exactly the approved steps, in the window.
The agent checks the result, attaches the evidence, and closes the ticket.
Works with ServiceNow · Red Hat Ansible Automation Platform · OpenShift · GitHub · OpenTofu · Grafana · Prometheus · Loki · Tenable · Qualys · Rapid7 · Splunk · Datadog · Dynatrace
Zero agent trust
Tickets, alerts, and tool output can carry an attacker's words, so the Silex AIOps Platform never relies on what the agent decides. The agent holds no real credentials, and six layers stand between it and production.
Autonomy ladder
A workflow moves from Assist to Act with approval, and then to Self-heal, only when its diagnoses match how your engineers resolved the same tickets and it passes its failure tests.
Agents investigate with read-only access and draft a diagnosis and a fix.
A person approves each change in one step; Ansible executes and verifies it.
Fixes you pre-approved as standard changes are applied, verified, and closed without waiting for a person. People audit.
Self-healing infrastructure
At Self-heal, a workflow applies, verifies, and closes the fixes you pre-approved as standard changes, like disk cleanup, service restarts, certificate renewals, and approved patch campaigns, without waiting for a person. Your engineers audit instead of approving each one.
You choose which fixes count as standard changes. Each run still files and closes its change in your ITSM, so the record matches one a person approved.
The gate holds every launch to the standard change's job templates, hosts, and window, and Ansible Automation Platform runs it. Nothing outside the template runs.
Every fix is checked before the ticket closes. A failed check backs out what it broke, and can open a problem, and an incident if service was left reduced.
A workflow reaches Self-heal only with a clean record at Act with approval, after passing our failure scenarios, and only when you sign the change. The off switch stops it at once.
Every self-healed change is in the audit and the weekly activity report, and the monthly service review covers how each self-healing workflow performed.
Evaluation
An agent that closes tickets has to be trusted with production. Silex tests models and agent harnesses in a lab built like an enterprise environment, with Ansible Automation Platform, ServiceNow change control, a runbook repository, and a blue-green three-tier application with UAT gates.
We test models from Anthropic, OpenAI, Google, and open-weight families, pick the model, reasoning level, and harness for each workflow, and re-test whenever a model changes. In production, every ticket a workflow works is compared with how your engineer resolved it.
What every run is graded on
Runs are graded from platform records, not from what the agent reports about itself.
Foundation
Silex is a Red Hat partner, and Red Hat Ansible Automation Platform is the platform's trusted execution layer. Agents never log in to hosts: every change runs as an approved job template under AAP's role-based access and policy as code. Silex has run enterprise Ansible programs since 2017, so the automation library the agents use is one our engineers build and maintain.
Red Hat Ansible Automation Platform · Event-Driven Ansible · AAP MCP server · OpenShift · OpenTofu
How we engage
A Patch Window Assessment or discovery workshop measures your advisory-to-fix time and maps the queue.
A triage agent works a test queue, then a share of live tickets, with read-only access.
Remediation, patching, and provisioning execute through job templates on one-step approval.
Workflows with a clean record run without per-change approval.
Managed operations: runs reviewed, models re-tested, and a monthly service review.
Day 2 with Silex
Go-live is one day. Managed operations keep every workflow tested, measured, and current for every week after it, with a named Silex coordinator and the engineers who run your workflows.
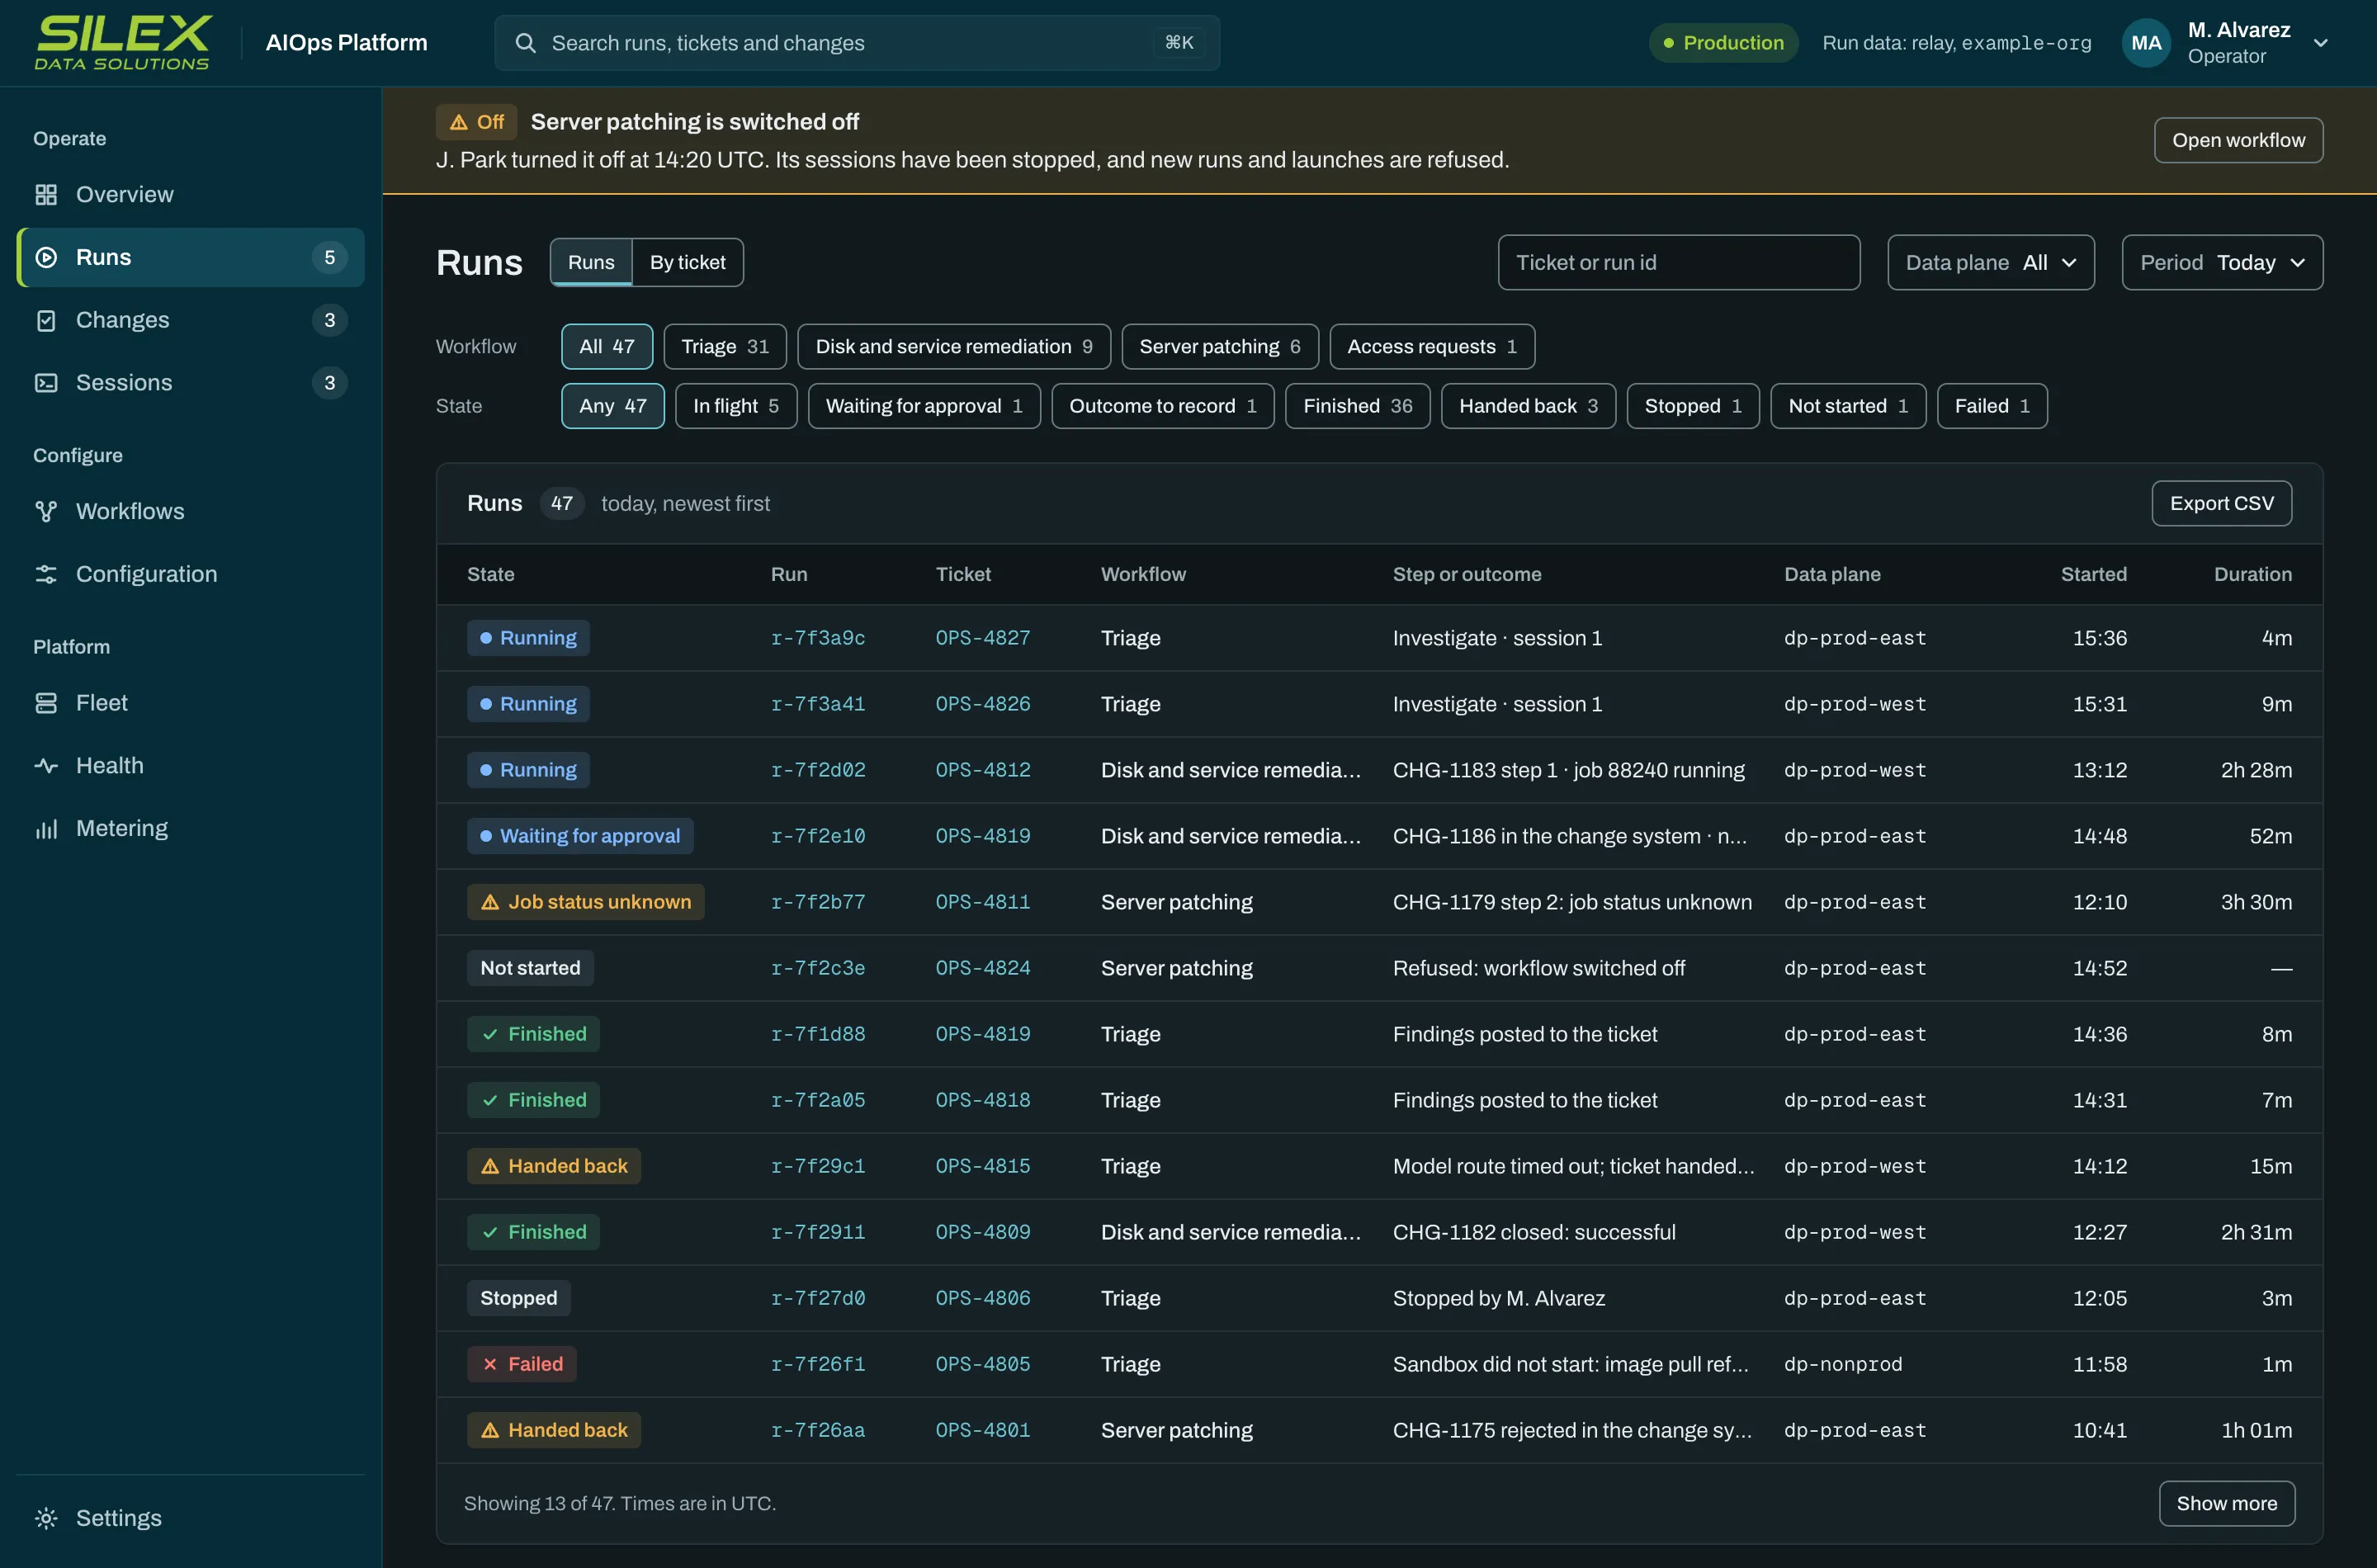
Review flagged runs and refusals, investigate failures, and pause or stop a workflow.
Prove every new model or agent version on the same tickets before it ships.
Track each workflow against its autonomy criteria and your ticket baseline.
Weekly activity, a monthly service review, and a quarterly governance review.
Keep integrations current as your platforms change, and add the work you rank next.
Questions buyers ask
No. Every workflow starts at Assist with read-only access. Changes need one-step human approval until a workflow has a clean record on your own tickets and passes its failure tests. You can stop any workflow at any time.
A workflow at Self-heal applies the fixes you pre-approved as standard changes, such as disk cleanup, service restarts, and certificate renewals, without waiting for a person. Each change is still filed in your ITSM, held to its job templates and window by the gate, run by Ansible Automation Platform, and verified or backed out. People audit the results instead of approving each one.
Agents act only through approved automation, so an automation platform is required. Silex builds on Red Hat Ansible Automation Platform and can stand it up or extend an existing installation.
We test models from Anthropic, OpenAI, Google, and open-weight families in our lab, then beside the current model on your own tickets, and pick the model for each workflow. Every model call passes the platform's model gateway on the route you choose, so it is budgeted and recorded.
In Silex's cloud, in your environment, or split between the two: full SaaS, hybrid with the data plane in your network, or self-hosted on your own OpenShift or Kubernetes. The controls and the audit are the same in every option.
The agent is treated as untrusted. It holds no real credentials, reaches your systems only through the platform's enforcement gateway, and changes a system only through a plan a person approved in your ITSM. The platform page explains the six layers of control.
Your ITSM and CMDB (for example ServiceNow), your monitoring and observability tools, and your vulnerability scanners. Vendor agents such as Tanium can be called through their MCP servers.
The assessment records your current advisory-to-fix time and queue wait times. Each phase reports time to resolve and the share of tickets the agents handle against that baseline.
Next step
The Patch Window Assessment measures how long a fix takes to reach production in your environment today and identifies the workflows where agents will shorten it first.